Getting Started
Provisioning on Control Hub
Use the Webex Control Hub to provision Agentic Apps for your organization. This includes configuring user access and authentication, and defining governance controls to manage which agentic capabilities are available to organizational users.
Users acknowledge and agree that they bear full responsibility for understanding, complying with, and managing all aspects of the liability framework related to their use of MCP applications.
This guide is for administrators only. This includes configuring user access and authentication, and defining governance controls to manage which agentic capabilities are available to organizational users.
anchorAccessing your Agentic Apps
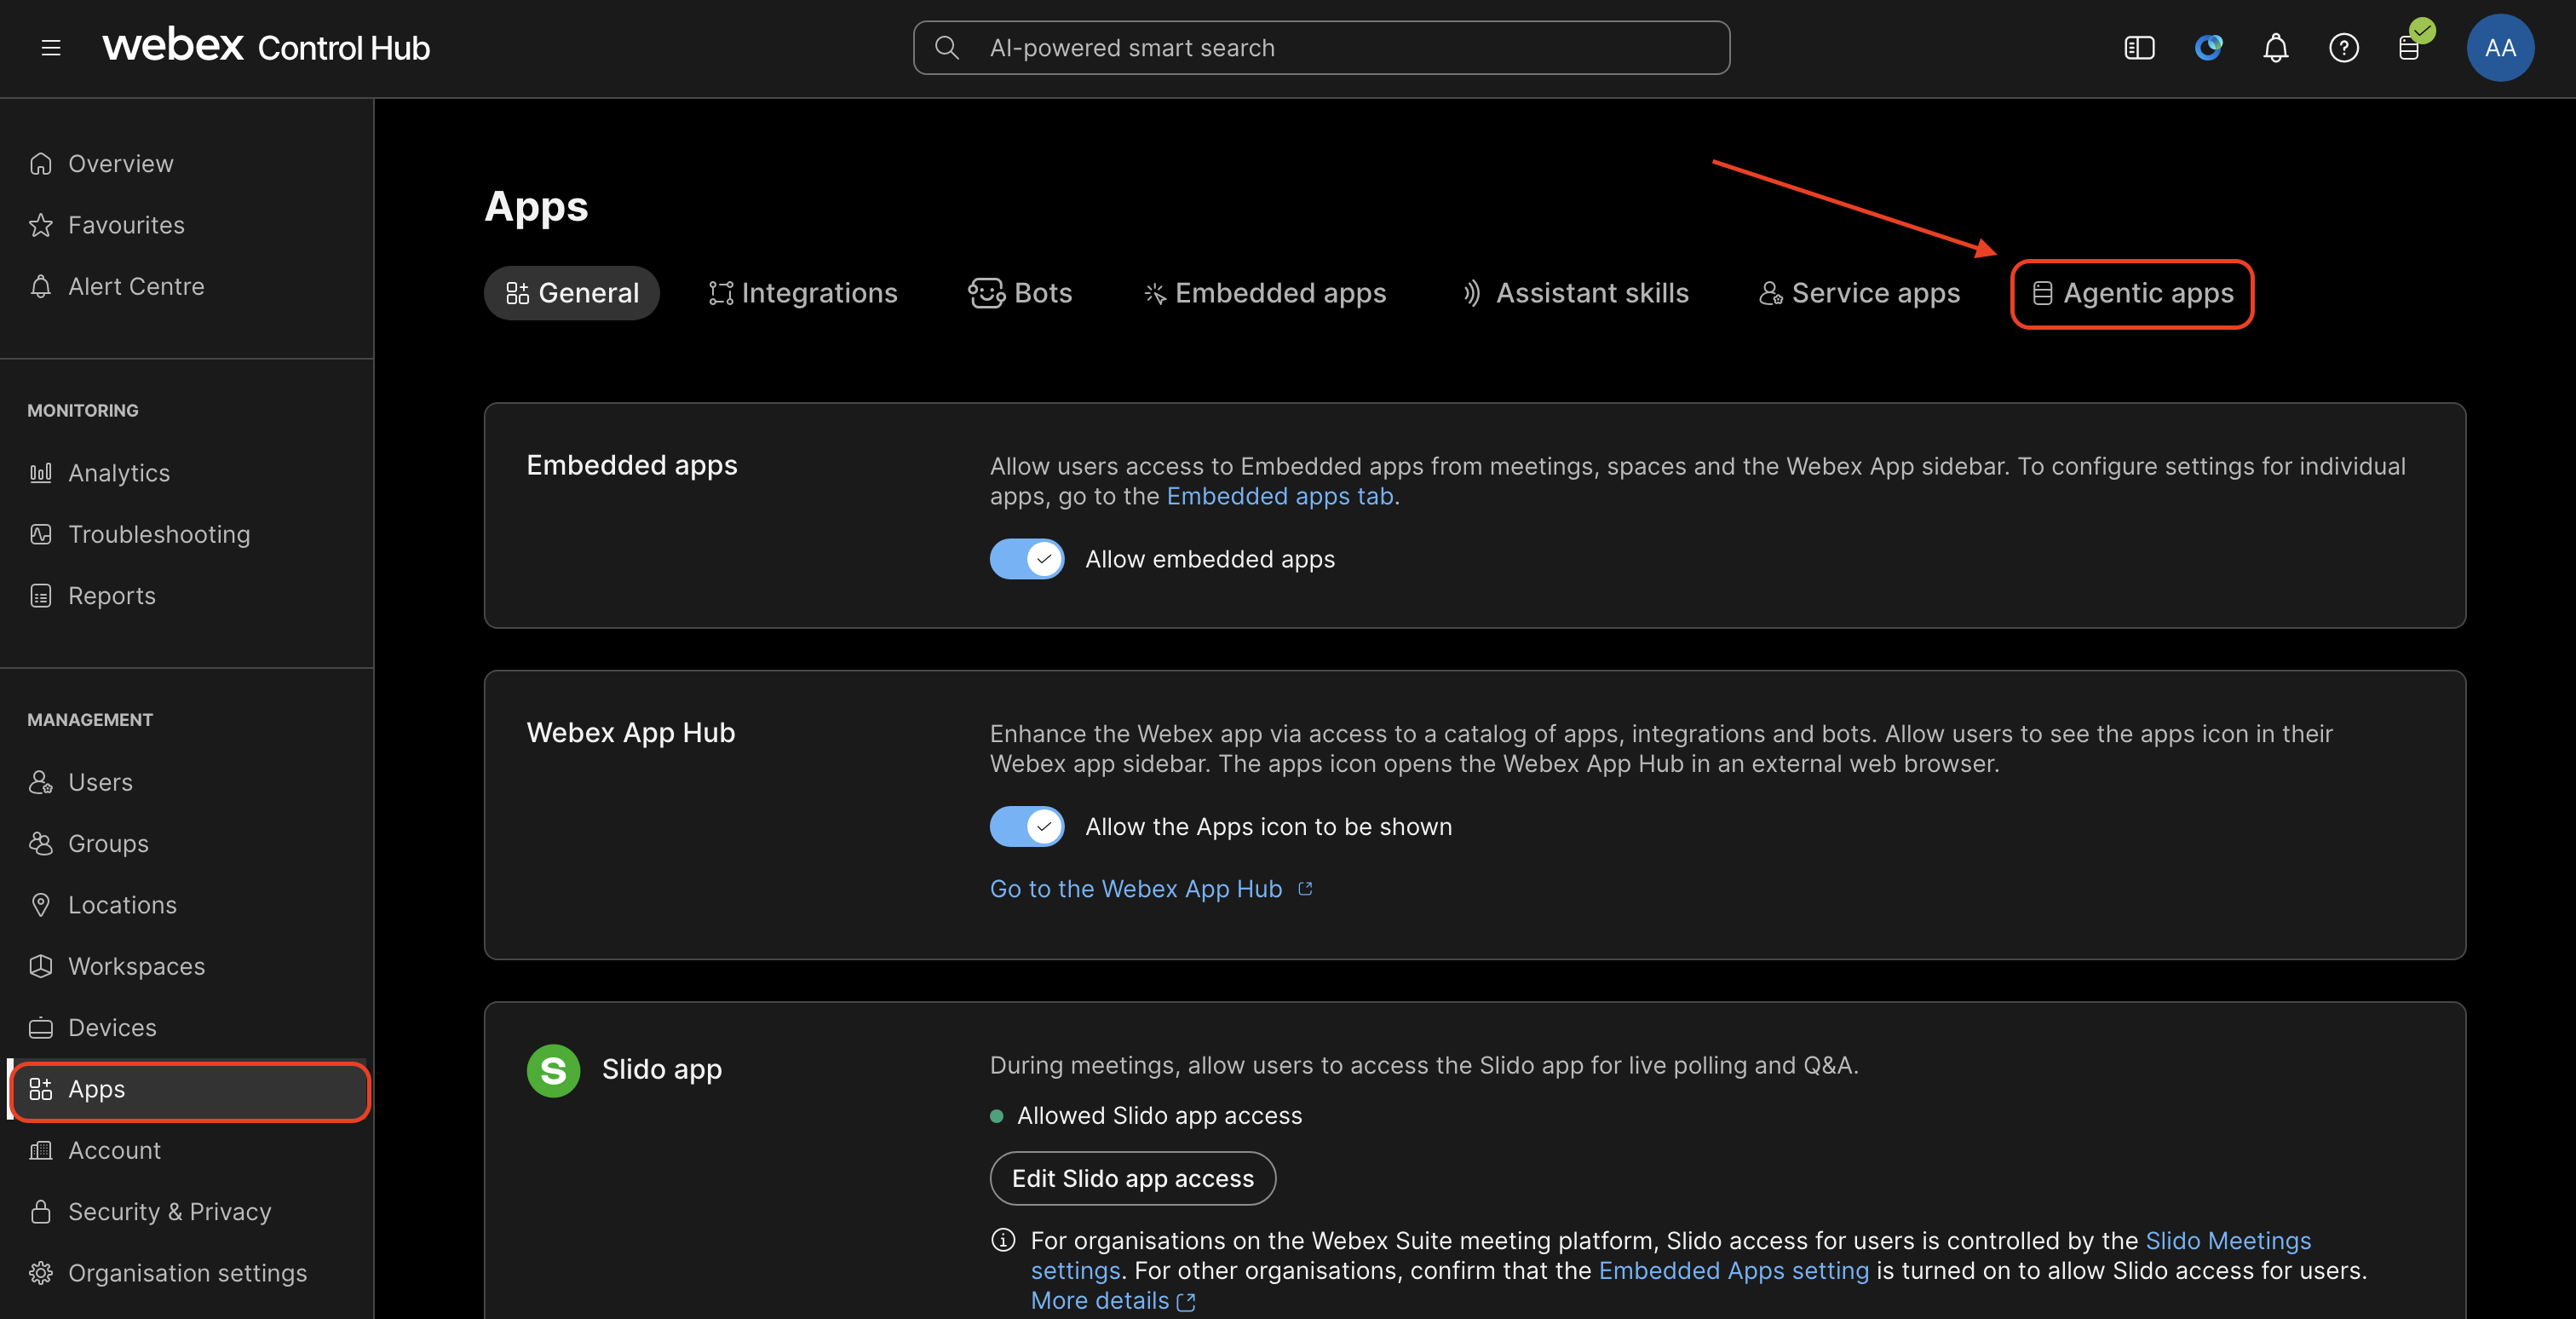
anchorIn Control Hub, go to Apps → Agentic Apps.
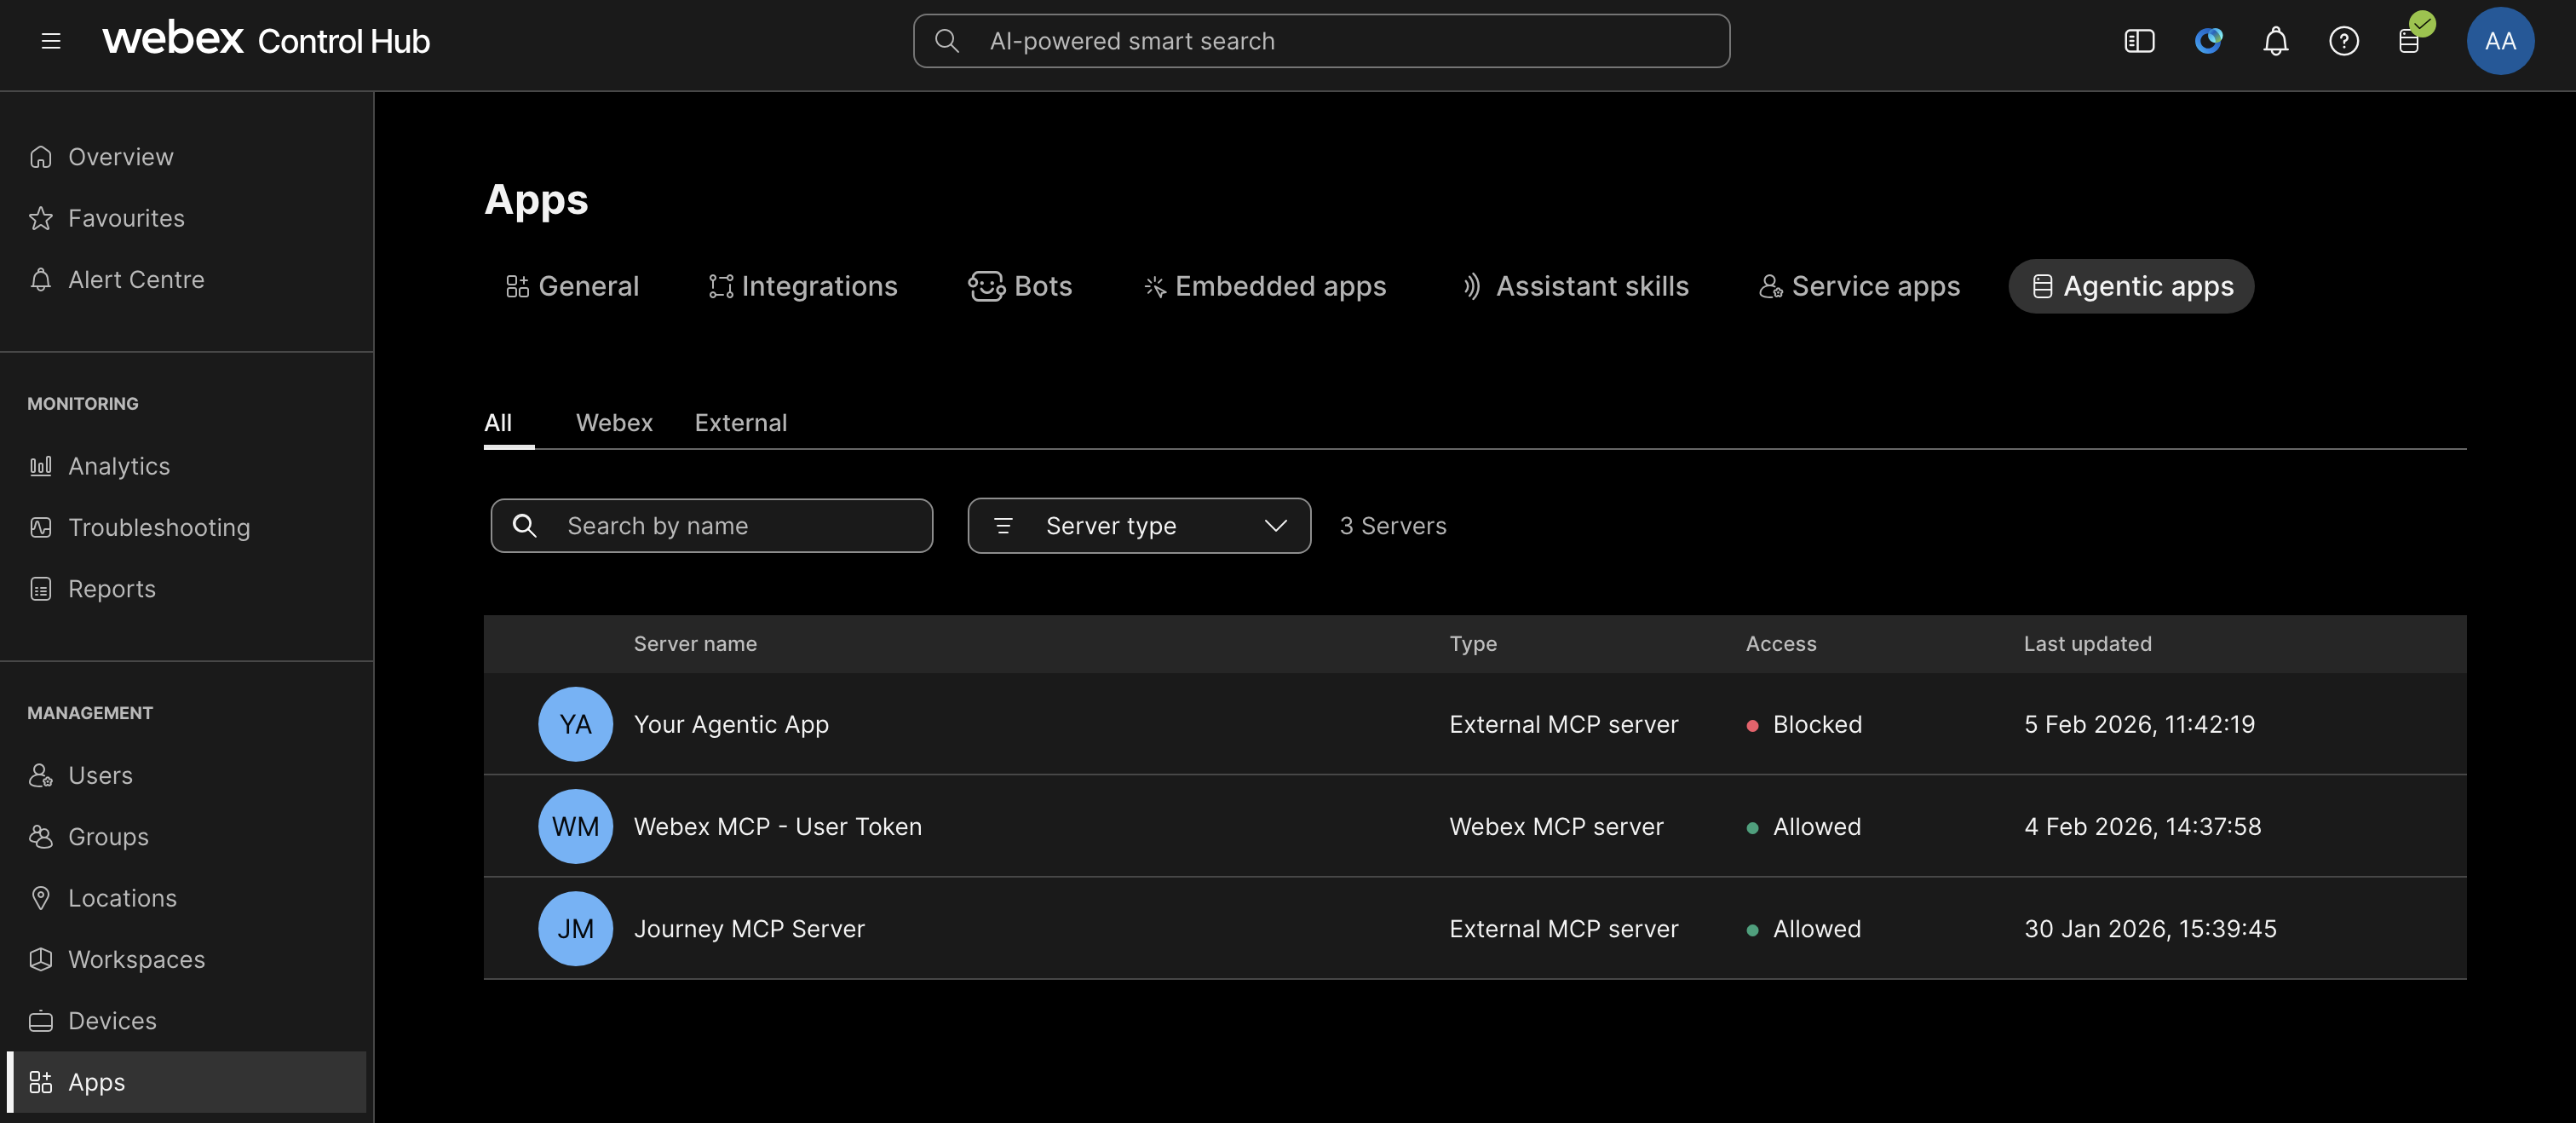
This page lists all public Agentic Apps along with the private apps which have been onboarded by users belonging to your organization.
anchorGeneral
anchorAfter selecting an app from the list, from the General tab, you can configure the app to be allowed or blocked for all users of your organization.
To restrict access to specific groups, select Selected user groups, choose the groups that should have access, and save your changes.
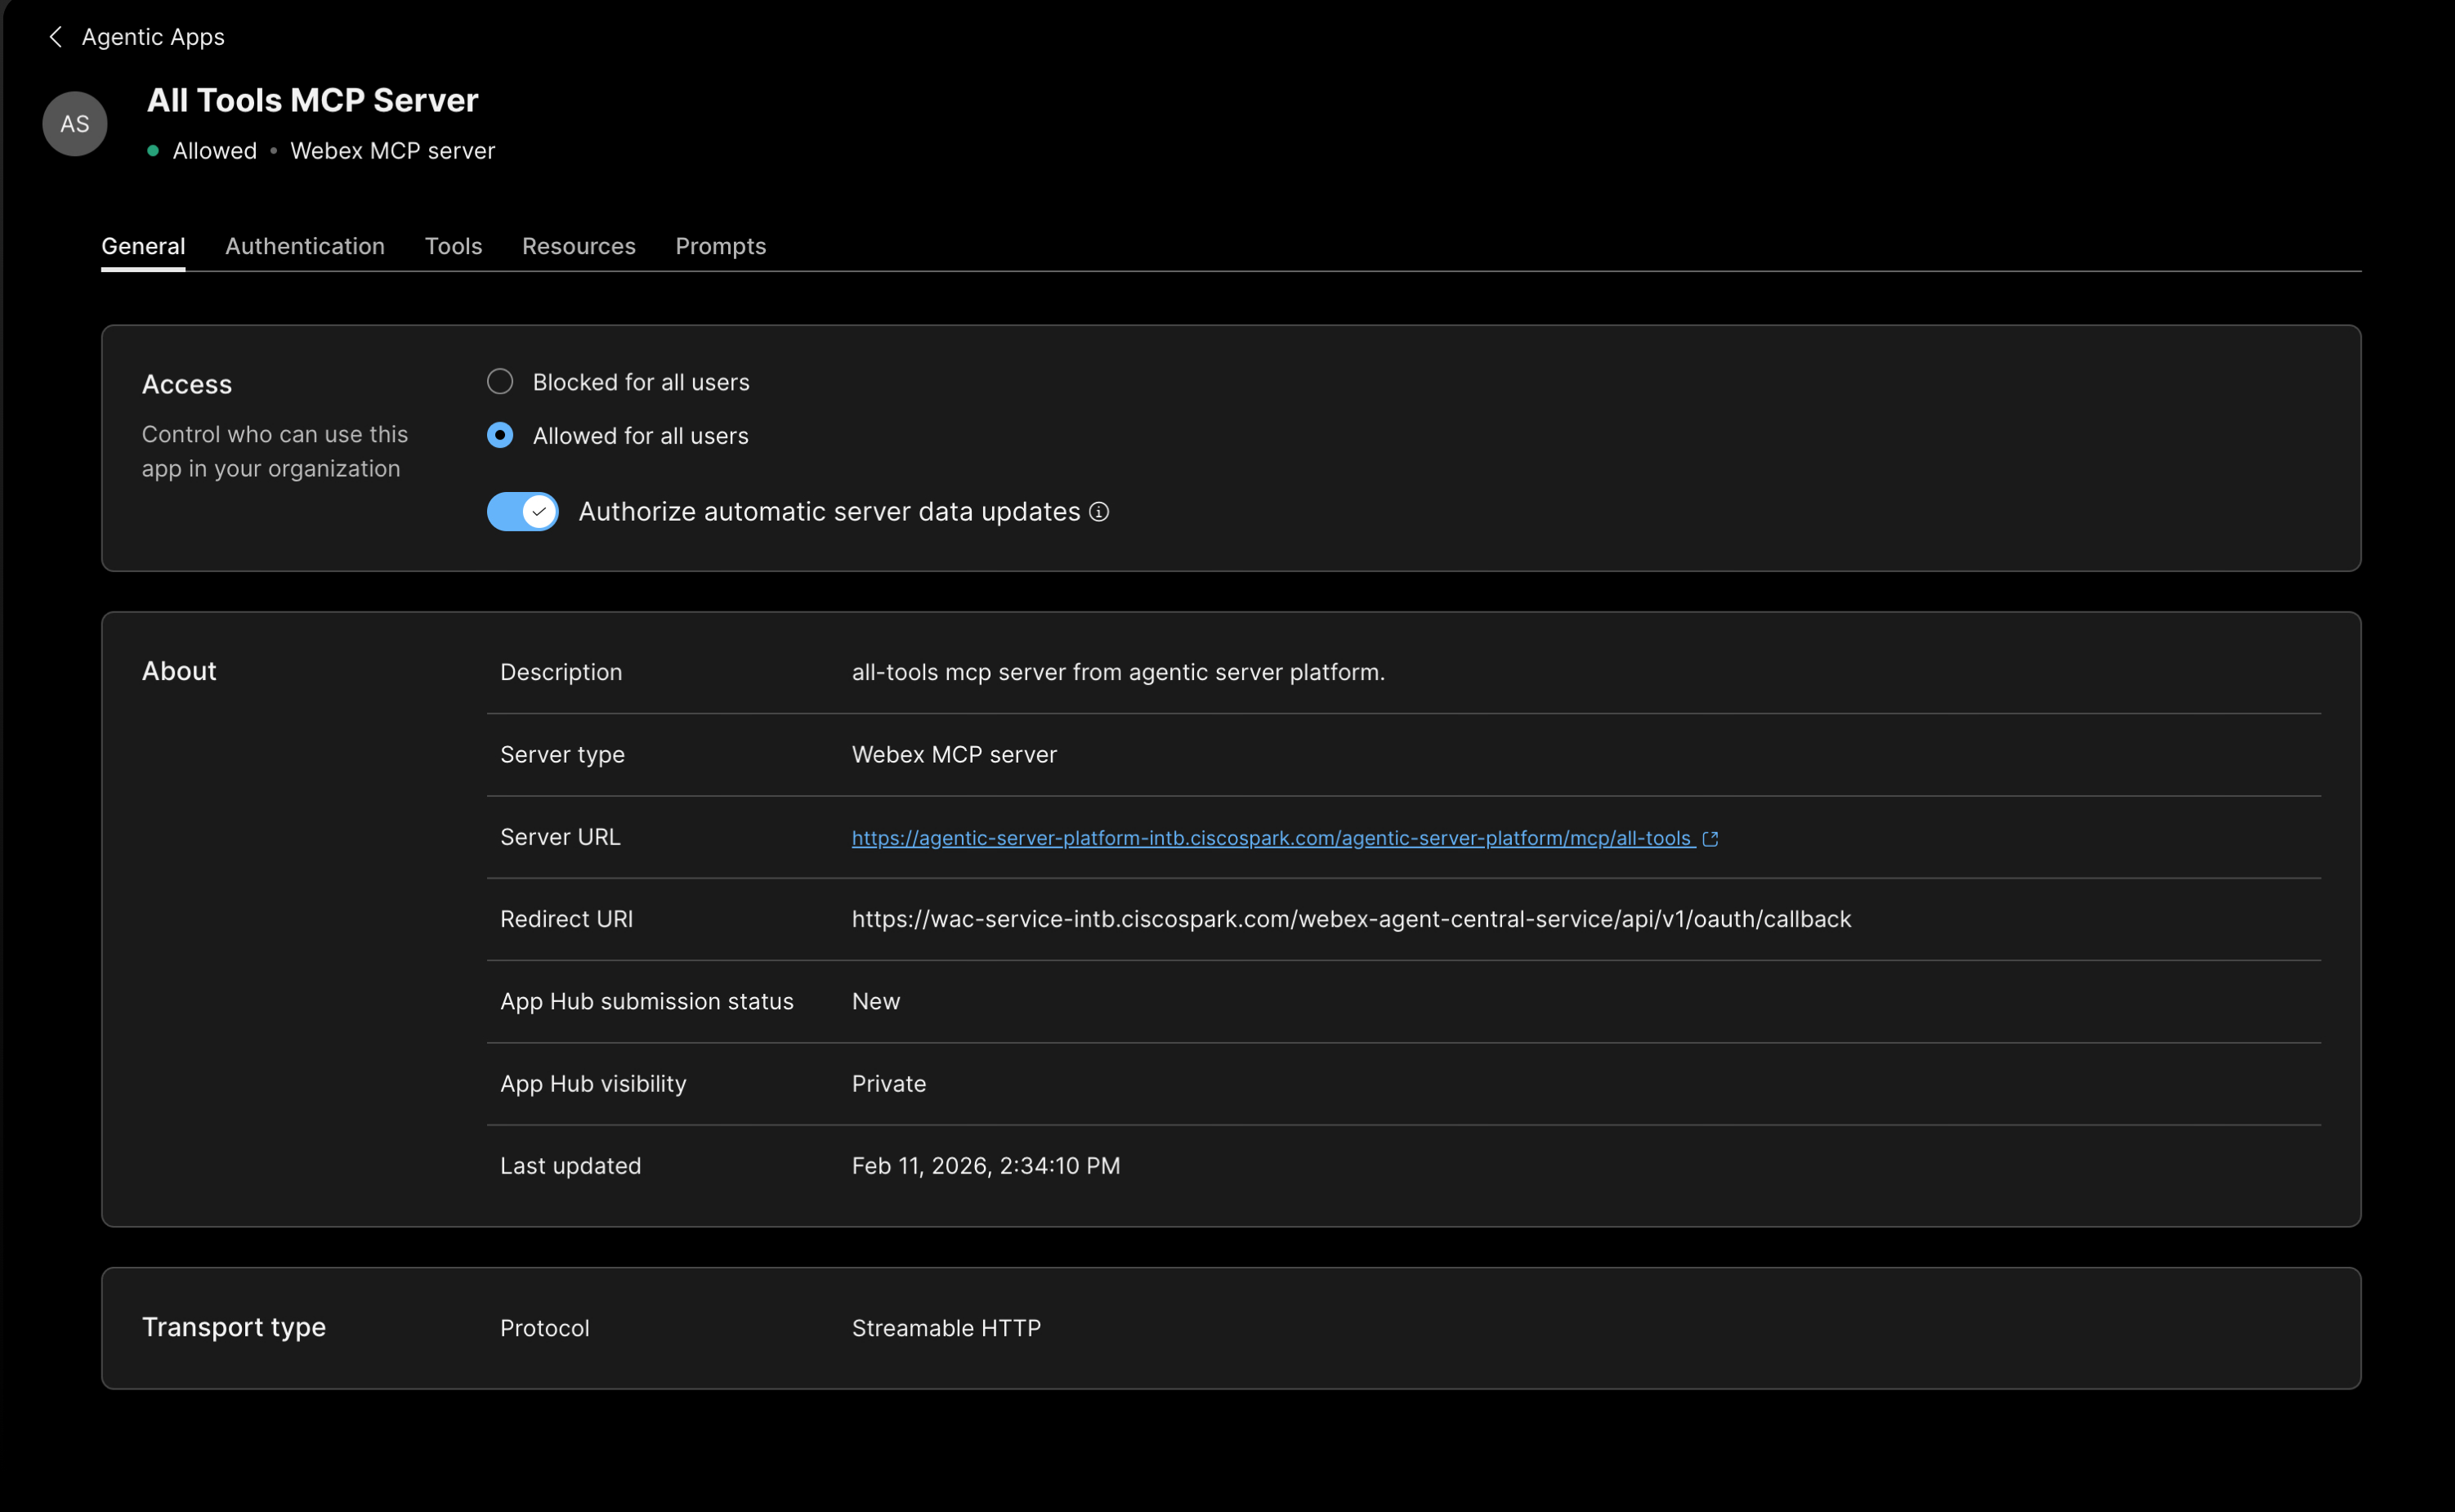
Authorize automatic server data updates - When enabled, updates to the server's name, description, URL (within the same domain), transport type, or other metadata do not require re-authorization before they take effect. However, the admin will see an indication that changes have occurred and can re-authorize at their discretion.
Group-Level Access
Group-level access for MCP servers gives enterprise administrators more granular control over who can access and use a specific server. Instead of enabling an MCP server for the entire organization, administrators can restrict access to selected user groups.
For MCP actions in Webex AI Agent Studio, group-level access is not supported; tool access is managed at the organization level.
anchorAuthentication
anchorCisco official servers are automatically configured. You should update the authentication settings mentioned below only if you need to change the default authentication.
The Authentication section asks users for details according to the configuration set in the Developer Portal. Supported methods:
| Method | What to provide |
|---|---|
| OAuth 2.0 – Client Credentials | Client ID, Client Secret, Authorization Server URL, Token Endpoint Auth Method, Scope |
| OAuth 2.0 – Authorization Code | Client ID, Client Secret, Registration Endpoint, Authorization Endpoint, Authorization Server URL, Token Endpoint Auth Method, Scope |
| User Token | No input required |
| API Key | The API key |
| Custom Headers | Up to five (5) key–value pairs |
| Webex Service App | No credentials. Select the associated Service App and review its requested scopes. |
For OAuth 2.0 – Client Credentials, the Token Endpoint Auth Method can be client_secret_basic or client_secret_post. For OAuth 2.0 – Authorization Code, it can be none, client_secret_basic, or client_secret_post.
Webex Service App
This method is available only for eligible Webex-hosted MCP servers that offer Webex Service App authentication. The administrator does not enter a client ID, client secret, or token.
To select the method and review its scopes:
- In Apps > Agentic Apps, select the MCP server and open the Authentication tab.
- For Authentication type, select Webex Service App.
- Select the Service Apps page link shown with the associated Service App.
- Review the Service App details and requested scopes, then follow Full Admin Authorization of a Service App to complete the separate authorization step.
If the requested scopes change later, Control Hub indicates that reauthorization is required. Review the updated scopes before reauthorizing the Service App.
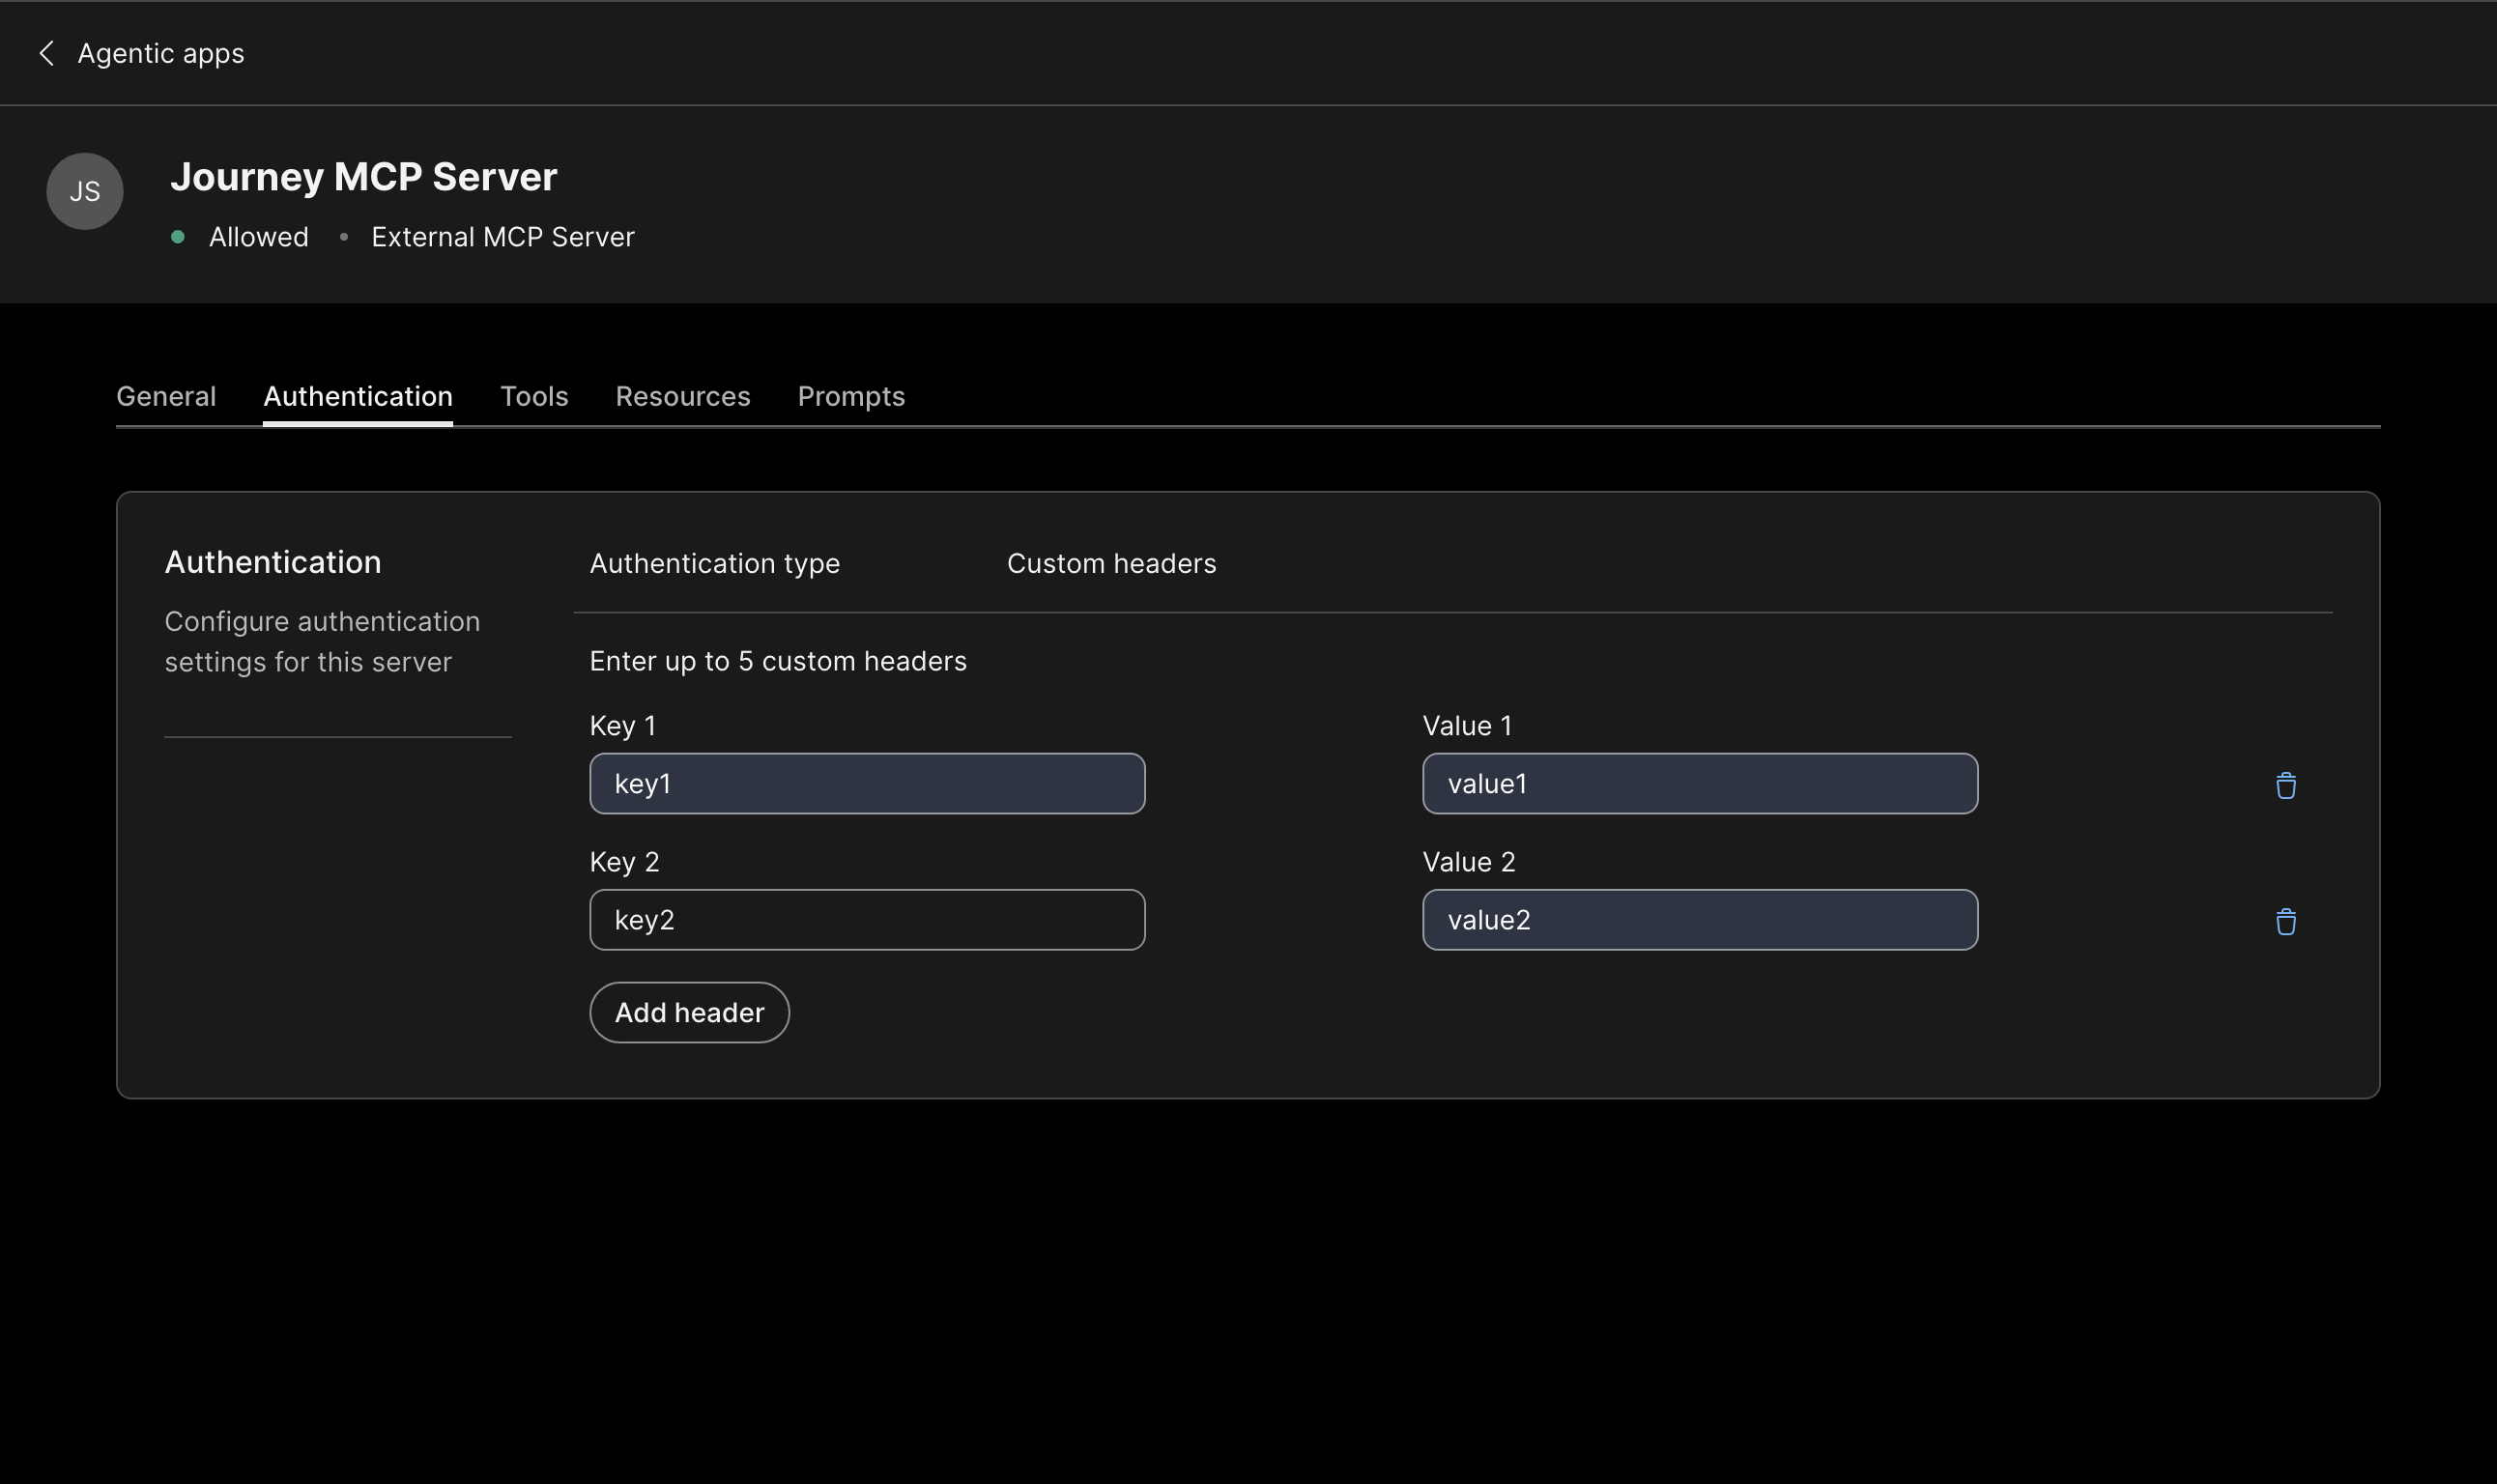
Custom Headers are configurable for all authentication types.
anchorCapabilities Configuration
anchorFor MCP Servers, you will see three tabs - one for Tools, one for Resources and one for Prompts.
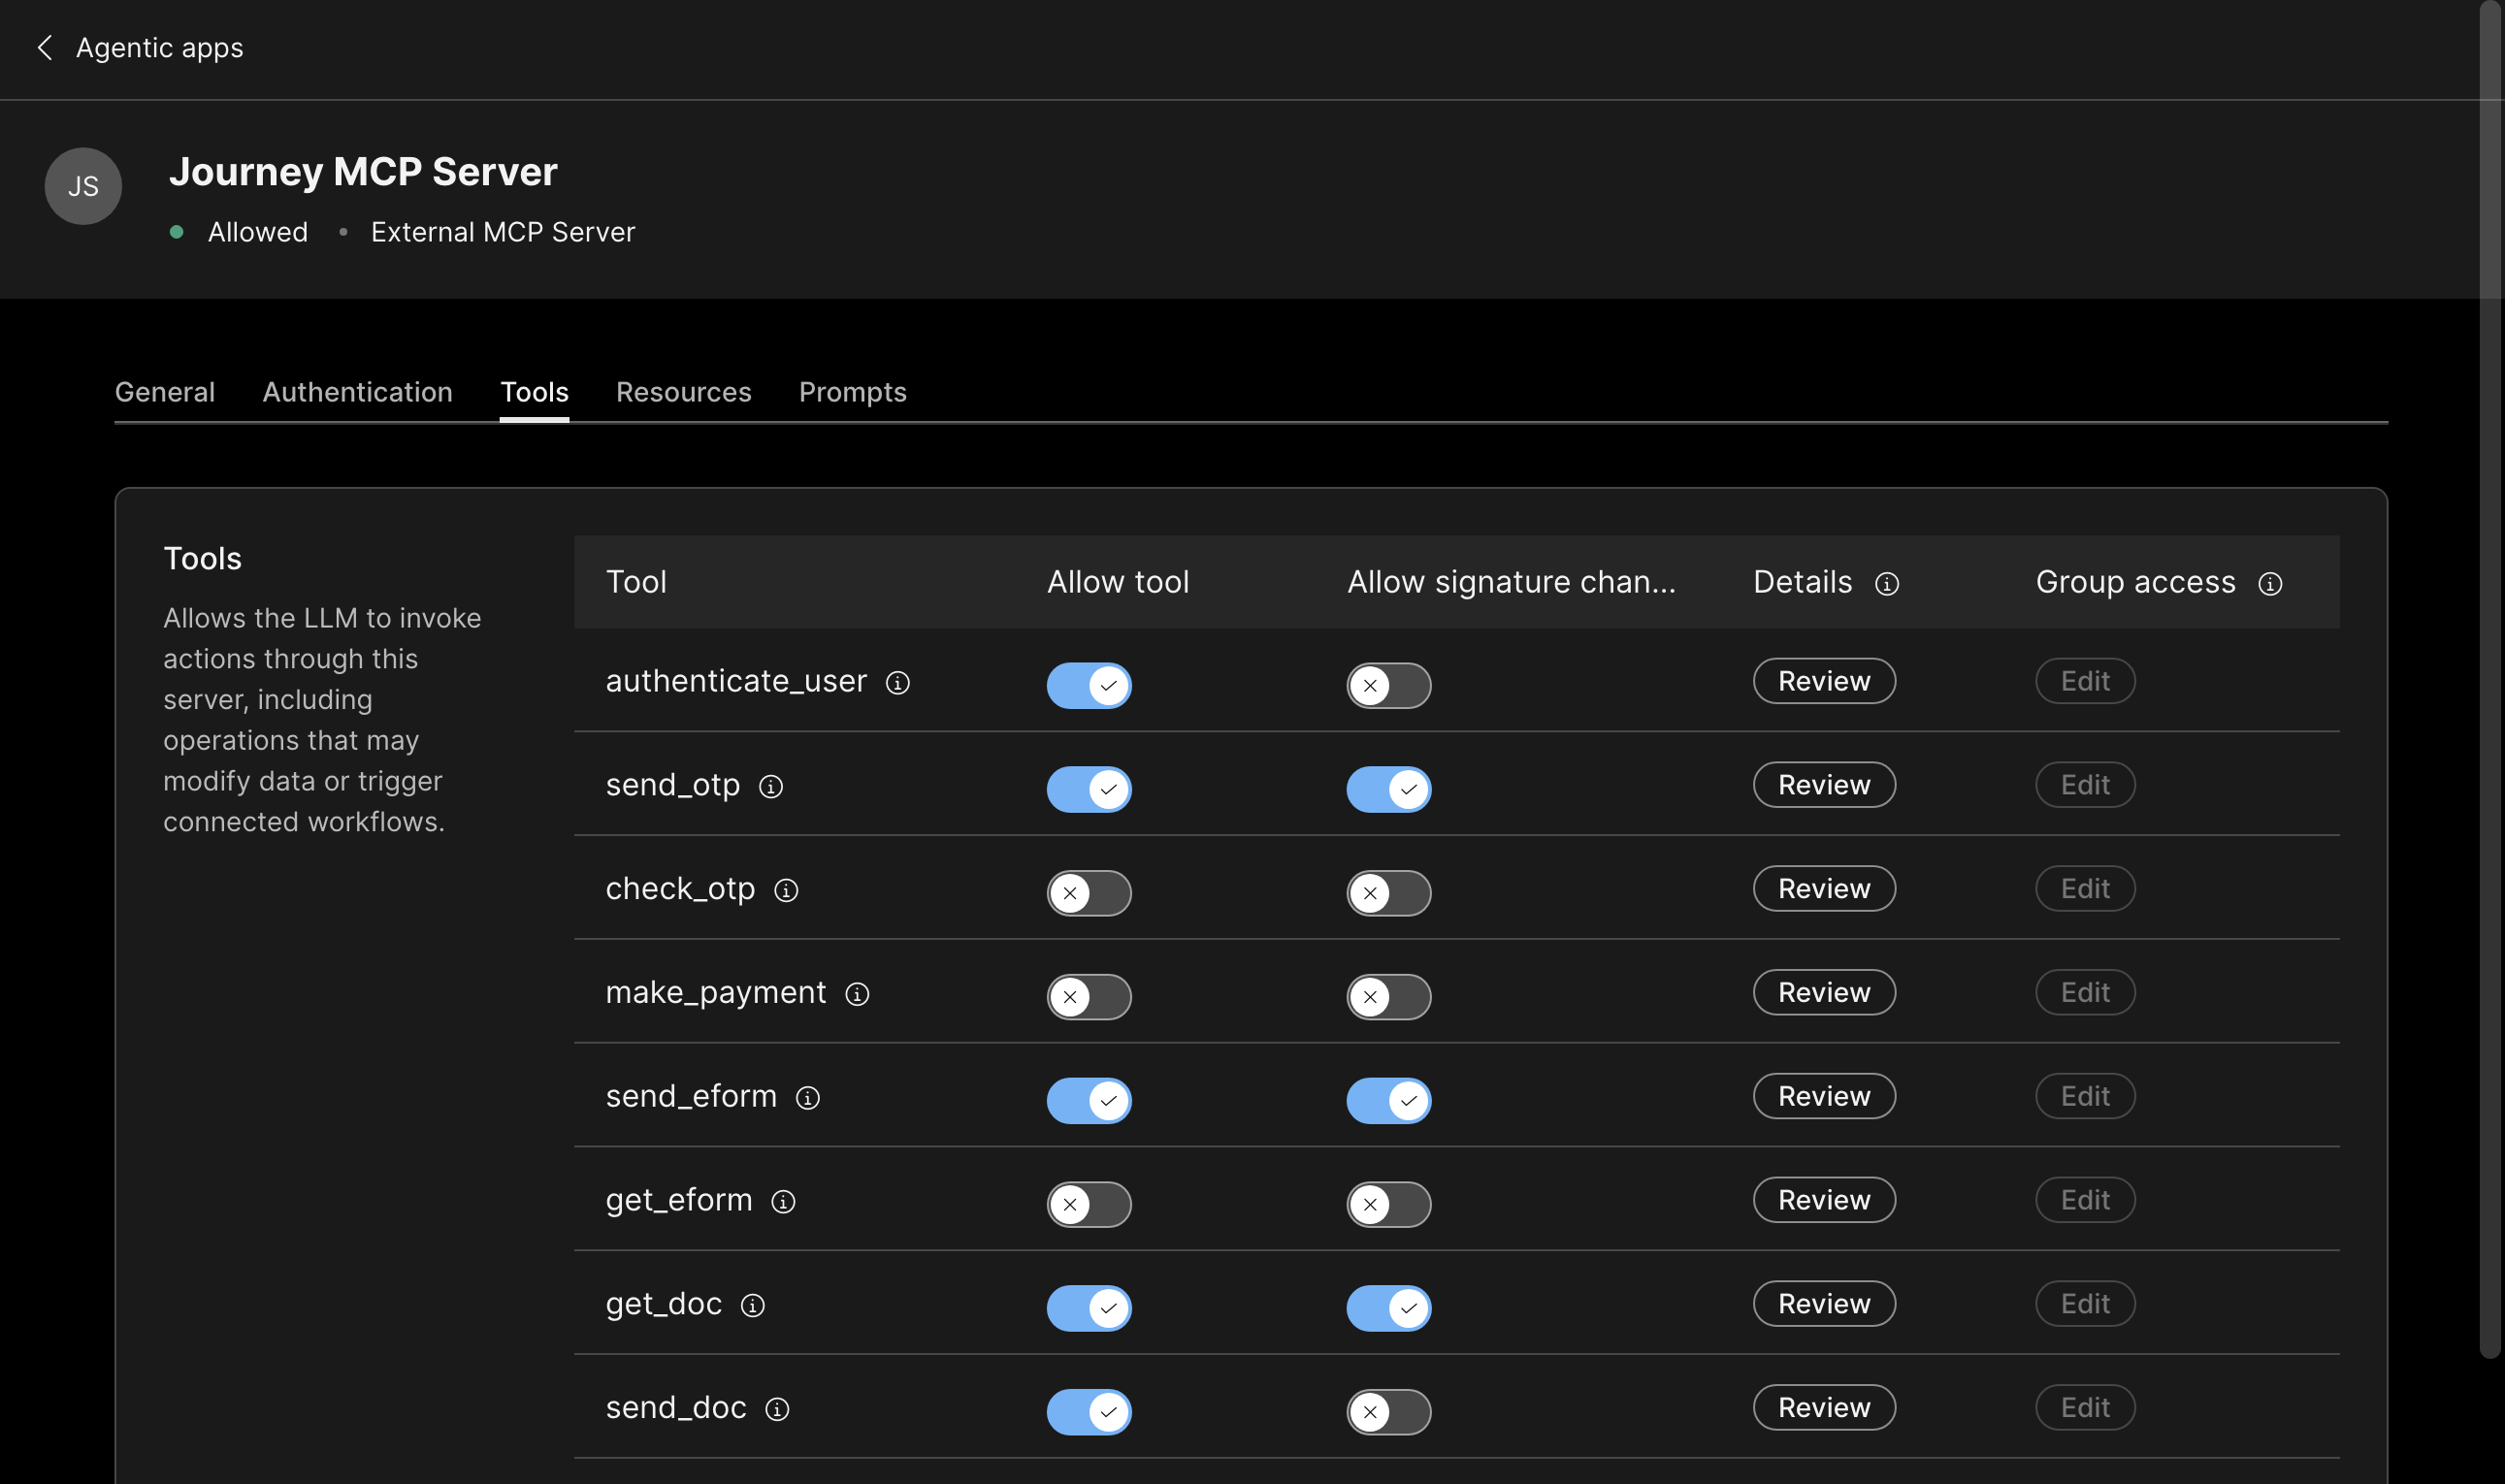
Tools
In the Tools section you can do the following:
- Enable tool: When a tool is enabled by the org admin, it becomes available to users on the client side. Users can discover and use the tool based on the access configured by the admin.
- Disable tool: When a tool is disabled by the org admin, it is no longer visible or available to users on the client side. This allows admins to restrict access to tools that should not be used within the organization.
- Signature change: When enabled, tools remain accessible to users even if the tool's schema changes after authorization. Org admins do not need to re-authorize each tool when its schema is updated by the developer. However, an indication is shown that the tool signature has drifted from what was originally approved.
- Review individual tool details: Admins can review the details of each tool, including its input schema, output schema, and annotations. This helps admins understand what data the tool accepts, what response it returns, and any additional metadata associated with the tool.
- Review and reauthorize schema changes: After an admin authorizes a server, any subsequent changes to tool schemas will require admin review and re-authorization. The admin must review the updated schema and re-authorize to update the approved baseline. This applies regardless of whether the tool signature change setting allows continued access - re-authorization is always needed to formally approve the new schema.
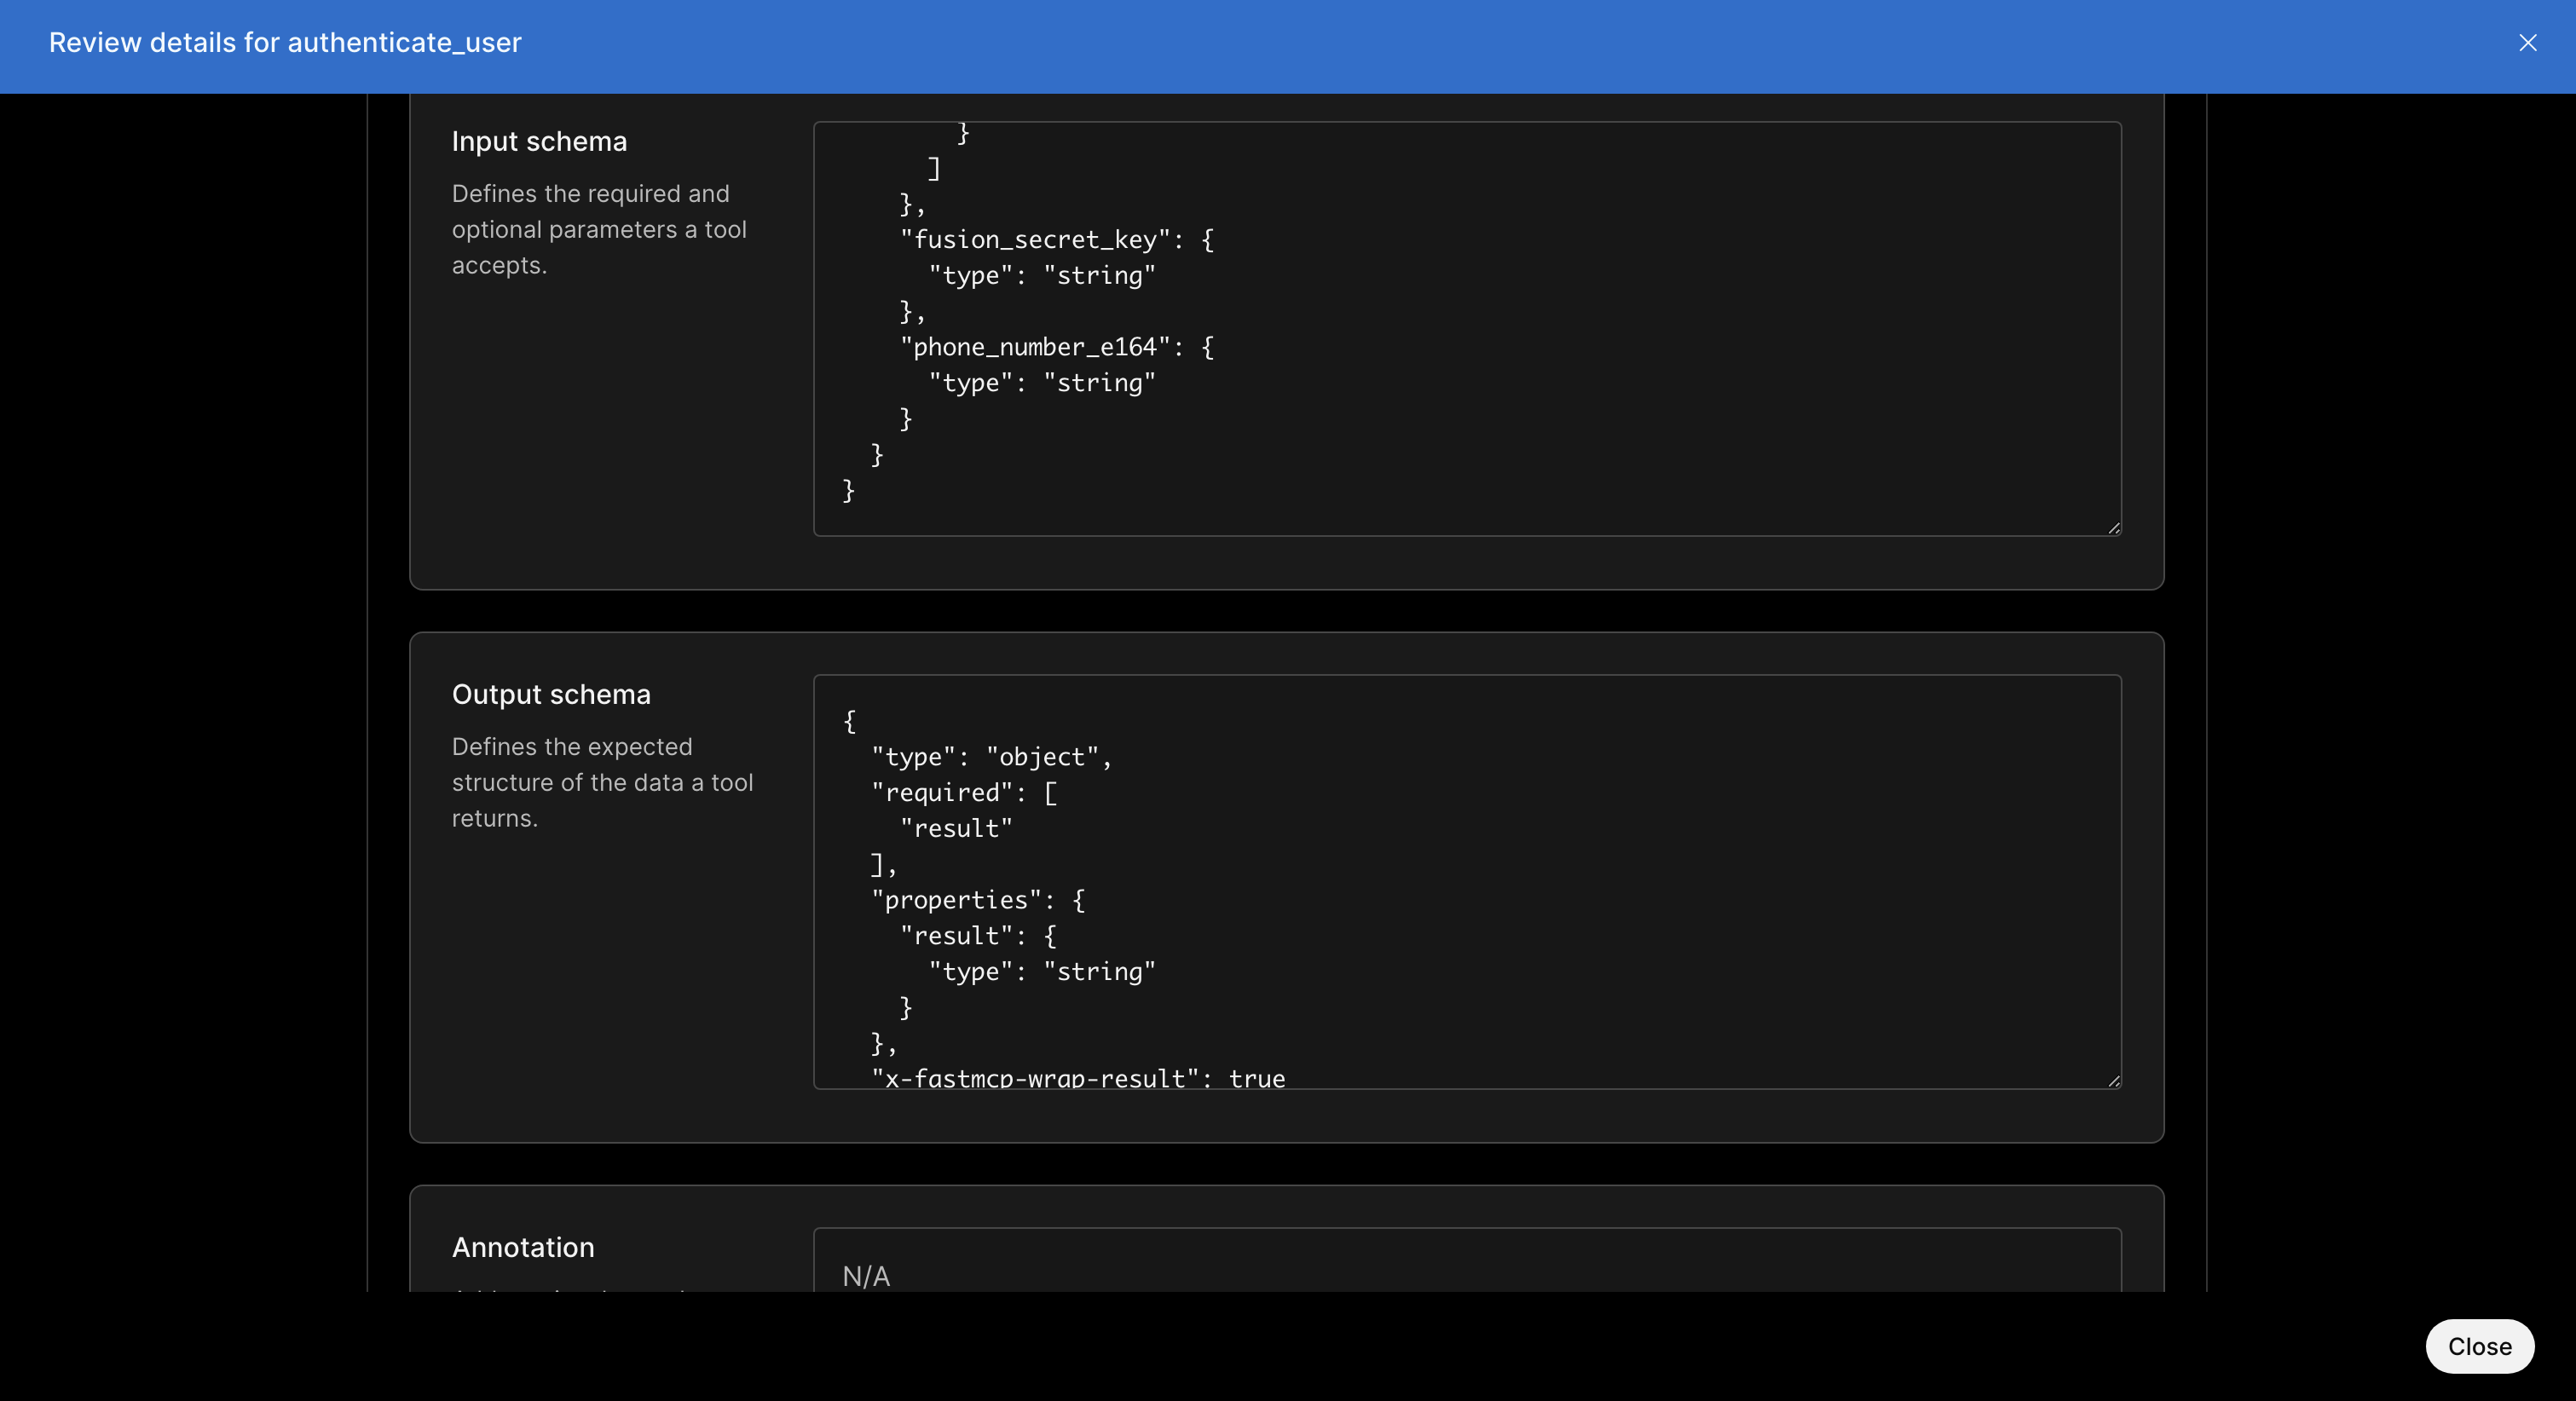
Similar functionalities are available in the Resources and Prompts pages.
anchorDeprecation Labels in Control Hub
anchorControl Hub supports end-to-end lifecycle management for MCP tools, resources, and prompts. Deprecated and Retired labels help administrators identify affected capabilities. Where available, Control Hub also displays retirement dates, replacement capabilities, and migration guidance so administrators can plan migrations before a capability is retired.
anchorRefreshing MCP Server Tools in Control Hub
anchorThe backend caches each MCP server's tool list for up to one hour. During this period, requests from Control Hub administrators or SDK clients return the cached list. After the cache expires, the next backend request retrieves the latest tools from the MCP server.